How Native CDR Works in GateScanner®
Content Disarm and Reconstruction (CDR) works differently than traditional detection-based security.
Rather than searching for malware, CDR eliminates any foreign code in incoming content, even without detection.
Here's how CDR is embedded natively into the GateScanner Mail Protection gateway.
Each incoming email and attachment is rebuilt from scratch — ensuring that only threat-free content is delivered to the inbox.
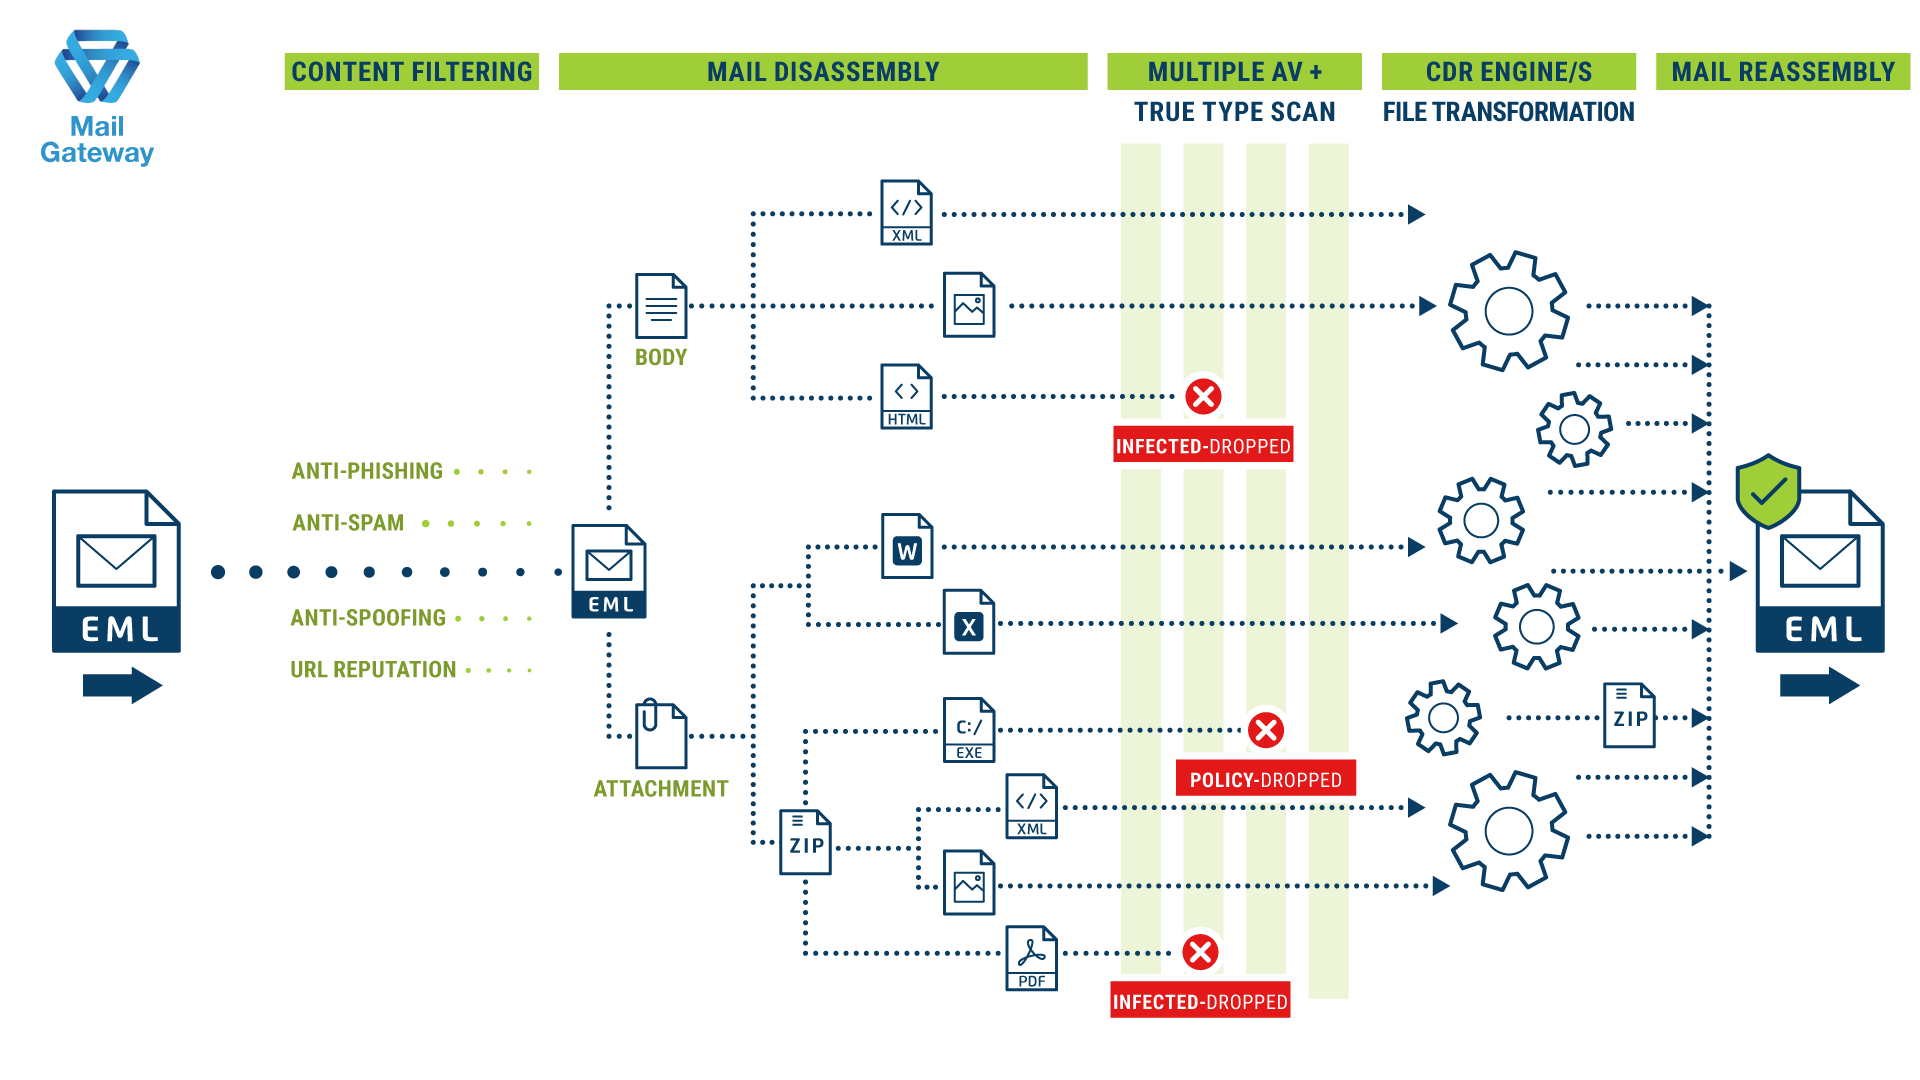
Step 1: Email Ingestion
The full email (including headers, body, embedded objects, and attachments) is ingested by GateScanner®.
Step 2: Deep Recursive Deconstruction
Attachments and email content are unpacked layer by layer — including archives, scripts, macros, and embedded files — recursively and without execution.
Step 3: Active Content Removal
All executable code, scripting, links, and other active elements are removed or neutralized at a binary level.
Step 4: Multiscanning
Each dissected email component is scanned using multiple leading antivirus engines, combining signature-based, heuristic, and static code analysis for unmatched detection coverage.
Step 5: Reconstruction & Delivery
Cleaned, policy-compliant versions of the content are reconstructed and reassembled into a new email package and safely delivered to the recipient.
